Publications
Execution-State-Aware LLM Reasoning for Automated Proof-of-Vulnerability Generation
Haoyu Li, Xijia Che, Yanhao Wang, Xiaojing Liao, Luyi Xing
arXiv preprint 2026 [Paper]
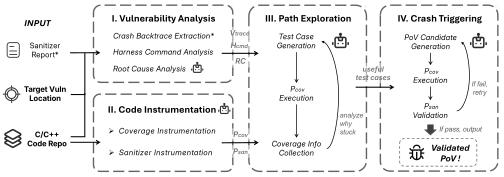
We present DrillAgent, an LLM agent that generates proofs-of-vulnerability via a hypothesize–verify–refine loop grounded in concrete execution states, solving up to 52.8% more CVEs on SEC-bench than prior agents.
BlueSWAT: A Lightweight State-Aware Security Framework for Bluetooth Low Energy
Xijia Che, Yi He, Xuewei Feng, Kun Sun, Ke Xu, Qi Li
ACM CCS 2024 [Paper] [Code] [Slide]
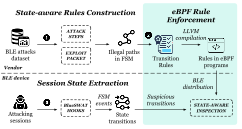
BlueSWAT detects BLE session-based attacks by modeling them as malicious paths in a finite state machine, and deploys rules as reboot-free eBPF patches, mitigating 76.1% of attacks with 0.073% memory overhead.
Cross Container Attacks: The Bewildered eBPF on Clouds
Yi He, Roland Guo, Yunlong Xing, Xijia Che, Kun Sun, Zhuotao Liu, Ke Xu, Qi Li
USENIX Security 2023 [Paper] [Code] [Slide] [Video]
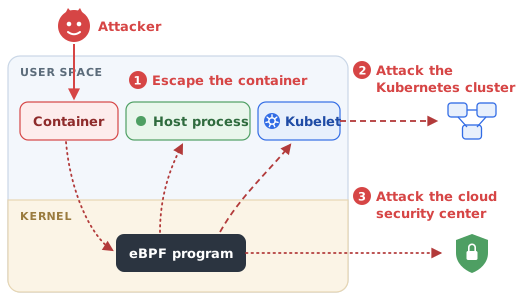
We show that eBPF tracing breaks container isolation, enabling data theft, DoS, and container escape. We compromised five online shell services, Google Cloud Shell, and Kubernetes services of three cloud vendors.
Blog
Confirming Claims of Superposition and Adversarial Examples in Toy Models
Xijia Che, Zephaniah Roe
Jul. 2026 [Blog] [LessWrong]

We replicate three core claims of Stevinson et al. in toy classifiers: PGD attacks match theoretical optima, robustness drops as superposition grows, and attacks transfer because feature geometry converges across runs.